Monday, April 29, 2024

Digital Forensics:Guidance for Incident Responders

Guidance for Incident Responders

Digital Forensics:Guidance for Incident Responders

 It includes the following topics:
  • AmCache’s contribution to forensic investigations: The AmCache registry hive’s role in storing information about executed and installed applications is crucial, yet it’s often mistakenly believed to capture every execution event. This misunderstanding can lead to significant gaps in forensic narratives, particularly where malware employs evasion techniques. Moreover, the lack of execution timestamp specificity in AmCache data further complicates accurate timeline reconstruction.
AmCache’s contribution to forensic investigations:
  • Browser forensics: Uncovering digital behaviors: The comprehensive analysis of browser artifacts is fraught with challenges, particularly regarding the interpretation of local file access records. The misconception that browsers do not track local file access can lead to significant oversight in understanding user behavior, underscoring the need for thorough and nuanced analysis of browser data.
  • The role of Link files and Jump Lists in forensics: Link, or LNK, files and Jump Lists are pivotal for documenting user behaviors. However, investigators sometimes neglect the fact that they’re prone to manipulation or deletion by users or malware. This oversight can lead to flawed conclusions. Furthermore, Windows’ automatic maintenance tasks, which can alter or delete these artifacts, add another layer of complexity to their analysis.
The role of Link files and Jump Lists in forensics

  • Prefetch files and program execution: Prefetch files’ role in improving application launch times and their forensic value in tracking application usage is well-documented. However, the common error of conflating the prefetch file’s creation date with the last execution date of an application leads to mistaken conclusions about usage patterns. Also, overlooking the aggregation of data from multiple prefetch files can result in a fragmented understanding of application interactions over time.
Prefetch files and program execution

  • ShellBags forensic analysis: ShellBags, with their ability to record user interactions with the File Explorer environment, offer a rich source of information. Yet not all investigators recognize that ShellBags track deleted and moved folders, in addition to current ones. This oversight can lead to incomplete reconstructions of user activities.
  • Shimcache’s forensic evolution: The Shimcache has long served as a source of forensic information, particularly as evidence of program execution. However, the changes in Windows 10 and later have significantly impacted the forensic meaning of Shimcache artifacts: indicating file presence, and not indicating execution. This misunderstanding can mislead investigators, especially since Shimcache logs the last modification timestamp, not execution time, and data is only committed to disk upon shutdown or reboot.
  • Forensic insights with SRUM: SRUM’s tracking of application execution, network activity, and resource consumption is a boon for forensic analysts. However, the wealth of data can also be overwhelming, leading to crucial details being missed or misinterpreted. For instance, the temporal discrepancies between the SRUM database and system logs can confuse investigators, making it challenging to align activities accurately. Additionally, the finite storage of SRUM data means older information can be overwritten without notice, a fact that’s often overlooked, resulting in gaps in data analysis.

Forensic insights with SRUM

  • The importance of User Access Logging (UAL): UAL’s tracking of user activities based on roles and access origins is essential for security analysis, especially since this feature is designed for Windows Server operating systems (specifically 2012 and later). Its vast data volume can be daunting, leading to potential oversight of unusual access patterns or lateral movements. Additionally, the annual archiving system of UAL data can cause confusion regarding the longevity and accessibility of logs, impacting long-term forensic investigations.
  • Decoding UserAssist for forensic evidenceThe UserAssist feature’s tracking of GUI-based program interactions is often misunderstood, with analysts mistakenly prioritizing run counts over focus time. This misstep can lead to inaccurate assumptions about application usage, as focus time—a more reliable indicator of execution—gets overlooked.
Decoding UserAssist for forensic evidence

Reference Microsoft Incident Response guide

หมายเหตุ:เนื้อหาในเว็บไซต์นี้มีขึ้นเพื่อวัตถุประสงค์ในการให้ข้อมูลและเพื่อการศึกษาเท่านั้น ช่วยเตือนความจำ

* หากมีข้อมูลข้อผิดพลาดประการใด ขออภัยมา ณ ที่นี้ด้วย  รบกวนแจ้ง Admin เพื่อแก้ไขต่อไป
ขอบคุณครับ

#WINDOWSFORENSIC #COMPUTERFORENSICS #DFIR #FORENSICS #DIGITALFORENSICS #COMPUTERFORENSIC #INVESTIGATION #CYBERCRIME #FRAUD 

Friday, April 5, 2024

Digital Forensics - Unlocking the Secrets

Digital Forensics - Unlocking the Secrets

Digital Forensics - Unlocking the Secrets

เมื่อ Cyber Threats คุกคาม และ Cyber Awareness อาจไม่เพียงพออีกต่อไป Digital Forensics (นิติวิทยาศาสตร์ทางดิจิทัล) จึงเป็นอีกหนึ่งทักษะความรู้ที่ทุกคนควรทราบ เพื่อให้เข้าใจเทคนิคและแนวทางปฏิบัติในการสืบสวนเพื่อหาหลักฐานนิติวิทยาศาสตร์ทางดิจิทัล ตลอดจนสามารถเข้าใจ จัดการ และจัดเก็บหลักฐานทางดิจิทัล (Digital Evidence) ที่สำคัญและมีความสมบูรณ์เพื่อให้สามารถนำไปใช้ในกระบวนการกฎหมายต่อไป

Digital Forensics - Unlocking the Secrets

วัตถุประสงค์:

  • เพื่อให้ผู้เรียนได้รับรู้และเข้าใจถึง Cyber Threats หรือ ภัยคุกคามทางไซเบอร์
  • เพื่อให้ผู้เรียนมีความรู้ความเข้าใจ Digital Forensics (นิติวิทยาศาสตร์ทางดิจิทัล) คืออะไร มีเทคนิค วิธีการ และแนวทางปฏิบัติในการสืบสวนเพื่อหาหลักฐานนิติวิทยาศาสตร์ทางดิจิทัลได้อย่างไร (Digital Forensics)
  • เพื่อให้ผู้เรียนเข้าใจว่าอะไรคือหลักฐานทางดิจิทัล (Digital Evidence) ประเภทของหลักฐานทางดิจิทัล และแนวทางการรวบรวมหลักฐานดิจิทัลที่ถูกต้องและสมบูรณ์เพื่อให้สามารถนำไปใช้ในกระบวนการกฎหมายต่อไป

ระยะเวลาการอบรม 1 วัน

Digital Forensics - Unlocking the Secrets

สถานที่อบรม


ที่มา:    https://swpark.or.th 
           

อ่่านเพิ่มเติม:  อบรม computer forensic.

หมายเหตุ:เนื้อหาในเว็บไซต์นี้มีขึ้นเพื่อวัตถุประสงค์ในการให้ข้อมูลและเพื่อการศึกษาเท่านั้น

* หากมีข้อมูลข้อผิดพลาดประการใด ขออภัยมา ณ ที่นี้ด้วย  รบกวนแจ้ง Admin เพื่อแก้ไขต่อไป
ขอบคุณครับ

#WINDOWSFORENSIC #COMPUTERFORENSICS #DFIR #FORENSICS #DIGITALFORENSICS #COMPUTERFORENSIC #INVESTIGATION #CYBERCRIME #FRAUD


Identifying uninstalled software using Event Logs with Osforensics

Identifying uninstalled software using Event Logs with Osforensics

Windows Event Logs are a detailed record of system, security, and application notifications and messages stored by the Windows operating system. These logs are invaluable for troubleshooting, monitoring system health, and analyzing security incidents.

Here's an overview of the main types of Windows Event Logs:

  1. Application Logs: These contain events logged by applications or programs. For example, a database application might record errors and significant operations here.

  2. Security Logs: These log security-related events, such as login attempts, resource access, and system changes. They are crucial for auditing and monitoring security-related activities.

  3. System Logs: These contain events logged by Windows system components. For example, drivers and services will log events here when they encounter issues or perform significant actions.

  4. Setup Logs: These are used for logging events related to the installation of applications or system components.

  5. Forwarded Events: These are events collected from remote computers and stored locally.

Windows Event Logs are stored at the following path: C:\Windows\System32\winevt\Logs

Osforensics V7 can be used to help identify uninstalled software. Open the Event Log Viewer from the Start screen in OSF…

Like many other actions and events recorded within the Windows Event Logs you can analyze these logs for records of uninstalled software. 

Identifying uninstalled software using Event Logs with Osforensics

You will first need to run a scan to search for any Event Logs that are located on a forensic image file or connected drive. Once complete, navigate to the Application event logs

Identifying uninstalled software using Event Logs with Osforensics


There will likely be tens of thousands of Application event logs on a system. To quickly identify logs that contain information about uninstalled software, use the Preset filtering options that are available in the drop-down menu
Identifying uninstalled software using Event Logs with Osforensics

Choose the ‘Software Package Removal Success’ preset which will then filter and present you with all logs with Event ID 11724 that deal with software uninstallation.


Identifying uninstalled software using Event Logs with Osforensics

In the example above, we can see that the software application ‘OpenVPN 2.6 was successfully uninstalled on 2/13/2024 at 10:29:29. Unfortunately, in our testing, this data is not comprehensive, meaning it does not seem to contain a complete historical list of uninstalled software.


อ่านเพิ่มเติม :


หมายเหตุ:เนื้อหาในเว็บไซต์นี้มีขึ้นเพื่อวัตถุประสงค์ในการให้ข้อมูลและเพื่อการศึกษาเท่านั้น

* หากมีข้อมูลข้อผิดพลาดประการใด ขออภัยมา ณ ที่นี้ด้วย  รบกวนแจ้ง Admin เพื่อแก้ไขต่อไป
ขอบคุณครับ

#WindowsForensic #ComputerForensics #dfir #forensics #digitalforensics #computerforensic #investigation #cybercrime #fraud

Friday, March 22, 2024

DIGITAL FORENSICS: BINWALK CTF

 DIGITAL FORENSICS: BINWALK CTF

Basic Cyber security

วันนี้แอดมาแนะนำหลักสูตร ด้านความมั่นคงปลอดภัยไซเบอร์ (Basic Cyber security) สำหรับผู้เริ่มต้นศึกษามี Lab ให้เล่น เป็นภาษาไทย และที่สำคัญคือ ฟรี


Binwalk command

Binwalk เป็นเครื่องมือที่ใช้ในการค้นหาไฟล์ binary เช่นภาพ, เสียงที่อยู่ภายใต้ไฟล์ รวมถึงไฟล์ zip ที่อยู่ภายใน binary ด้วยเช่นกัน โดยปกติมักจะใช้ใน firmware analysis


Download the file below and try to find the answer.


ข้อความถูกซ่อนอยู่ในภาพ

$ binwalk -M crypto5-binwalk.jpg
 คำสั่งที่ใช้ scanไฟล์ที่อยู่ในไฟล์ crypto5-binwalk.jpg ว่ามีไฟล์ชนิดไหนบ้าง
To scan the files Recursively
 .

 คำสั่งที่ใช้แตกไฟล์ที่อยู่ในไฟล์ firmware
$ binwalk -e crypto5-binwalk.jpg
To extract known file types from the firmware image
DIGITAL FORENSICS: BINWALK CTF


ไฟล์ 3029b.zip , secret.jpg   ที่ถูกแตกออกมา

DIGITAL FORENSICS: BINWALK CTF

Flag{...}

DIGITAL FORENSICS: BINWALK CTF

DIGITAL FORENSICS: BINWALK CTF


นอกจากนี้ยังเข้าไปที่ Online Binwalk Utility

DIGITAL FORENSICS: BINWALK CTF

DIGITAL FORENSICS: BINWALK CTF

อ่านเพิ่มเติม


ที่มา: https://play.mooc.ncsa.or.th


หมายเหตุ:เนื้อหาในเว็บไซต์นี้มีขึ้นเพื่อวัตถุประสงค์ในการให้ข้อมูลและเพื่อการศึกษาเท่านั้น

* หากมีข้อมูลข้อผิดพลาดประการใด ขออภัยมา ณ ที่นี้ด้วย  รบกวนแจ้ง Admin เพื่อแก้ไขต่อไป
ขอบคุณครับ

#WindowsForensic #ComputerForensics #dfir #forensics #digitalforensics #computerforensic #investigation #cybercrime #fraud

Friday, March 8, 2024

ความรู้ที่ใช้ในการขอรับใบอนุญาต ประกอบวิชาชีพวิทยาศาสตร์และเทคโนโลยีควบคุม สาขานิติวิทยาศาสตร์

ความรู้ที่ใช้ในการขอรับใบอนุญาต ประกอบวิชาชีพวิทยาศาสตร์และเทคโนโลยีควบคุม สาขานิติวิทยาศาสตร์

จัดสอบวิชาชีพวิทยาศาสตร์และเทคโนโลยีควบคุม สาขานิติวิทยาศาสตร์

ใบประกอบวิชาชีพ

วิทยาศาสตร์และเทคโนโลยีควบคุม คือ ใบอนุญาตประกอบวิชาชีพเกี่ยวกับวิทยาศาสตร์และเทคโนโลยีควบคุม โดยแบ่งตามสาขา

ความสำคัญของใบประกอบวิชาชีพวิทยาศาสตร์และเทคโนโลยีควบคุม

บุคคลที่จะประกอบวิชาชีพที่ต้องใช้ความรู้และทักษะทางวิทยาศาตร์และเทคโนโลยี มีความจำเป็นอย่างยิ่งที่ต้องได้รับใบอนุญาตเป็นผู้ประกอบวิชาชีพวิทยาศาสตร์ และเทคโนโลยีควบคุมจากสภาวิชาชีพวิทยาศาสตร์และเทคโนโลยีควบคุม (สวทช.) ทั้งนี้ เพื่อให้มาตรฐานการประกอบอาชีพเป็นไปตามหลักสากล และเพิ่มความน่าเชื่อถือในการประกอบอาชีพอีกด้วย

วิชาชีพวิทยาศาสตร์และเทคโนโลยีควบคุม สาขานิติวิทยาศาสตร์

1. ความรู้พื้นฐานด้านนิติวิทยาศาสตร์

(1) หลักการทางนิติวิทยาศาสตร

หลักการทางนิติวิทยาศาสตร์ Digital Forensic

(2) การตรวจหา ตรวจค้น เก็บรักษา และตรวจวิเคราะห์วัตถุพยาน 
การตรวจหา ตรวจค้น เก็บรักษา และตรวจวิเคราะห็วัตถุพยาน

(3) การดูแลรักษาห่วงโซ่วัตถุพยาน 
วิชาชีพวิทยาศาสตร์และเทคโนโลยีควบคุม สาขานิติวิทยาศาสตร์

(4) ความปลอดภัยในการปฏิบัติงาน 
วิชาชีพวิทยาศาสตร์และเทคโนโลยีควบคุม สาขานิติวิทยาศาสตร์

วิชาชีพวิทยาศาสตร์และเทคโนโลยีควบคุม สาขานิติวิทยาศาสตร์

(6) ระบบบริหารคุณภาพด้านนิติวิทยาศาสตร์ตามมาตรฐานสากล 

วิชาชีพวิทยาศาสตร์และเทคโนโลยีควบคุม สาขานิติวิทยาศาสตร์

2. ความรู้เฉพาะด้านนิติวิทยาศาสตร์

  1. การตรวจพิสูจน์ทางพิษวิทยาและสารเสพติดวิชาชีพวิทยาศาสตร์และเทคโนโลยีควบคุม สาขานิติวิทยาศาสตร์
  2. การตรวจพิสูจน์ทางชีววิทยาและสาร พันธุกรรมมนุษย์
วิชาชีพวิทยาศาสตร์และเทคโนโลยีควบคุม สาขานิติวิทยาศาสตร์
     3.การตรวจพิสูจน์เทคโนโลยี สารสนเทศ
หลักการทางเทคโนโลยีสารสนเทศและ วิทยาศาสตร์คอมพิวเตอร์ในกระบวนการ นิติดิจิทัลสำหรับการตรวจค้น จัดเก็บ วิเคราะห์พยานหลักฐานนิติดิจิทัล และ รายงานผลข้อเท็จจริง 

3.1 เทคโนโลยีสารสนเทศสำหรับนิติวิทยาศาสตร์
3.2 การจัดเก็บและการสืบค้นข้อมูลสำหรับการ สืบสวนอาชญากรรม 
3.3 ฐานข้อมูล 
3.6 โครงสร้างระบบคอมพิวเตอร์และ ระบบปฏิบัติการ  
    - macOS Forensics 
   - เทคโนโลยีการสื่อสารเคลื่อนที่ 
3.8 อื่น ๆ ที่เกี่ยวข้อง  

** การตรวจพิสูจน์เทคโนโลยีสารสนเทศ  1. กรณีมีความรู้ด้านการตรวจพิสูจน์เทคโนโลยีสารสนเทศมาแล้ว โดยมีใบประกาศนียบัตรผ่านการอบรมใน รายวิชาข้อ 3.1-3.6 จากในประเทศหรือต่างประเทศมาแสดง ให้อบรมเพิ่มเติมจำนวน 18 ชั่วโมง ในรายวิชา ข้อ 3.7 จำนวน 15 ชั่วโมง และข้อ 3.8 จำนวน 3 ชั่วโมง 2. กรณีไม่มีความรู้ด้านการตรวจพิสูจน์เทคโนโลยีสารสนเทศมาก่อนต้องเข้ารับการอบรมจำนวน 24 ชั่วโมง 

อ้างอิงจาก: ประกาศสภาวิชาชีพวิทยาศาสตร์และเทคโนโลยี ที่ 4/2566 เรื่อง หลักเกณฑ์ และวิธีการยื่นขอเป็นหน่วยงานจัดอบรม ผู้ขอรับใบอนุญาตประกอบวิชาชีพวิทยาศาสตร์และเทคโนโลยีควบคุม สาขานิติวิทยาศาสตร์

สภาวิชาชีพวิทยาศาสตร์และเทคโนโลยี

อ่านเพิ่มเติม:


อ้างอิงจาก:
  • ใบประกอบวิชาชีพ วิทยาศาสตร์และเทคโนโลยี , chulatutor ,27,มี.ค,2567
  • องค์ความรู้ด้านนิติวิทยาศาสตร์ของผู้ขอรับใบอนุญาต ประกอบวิชาชีพวิทยาศาสตร์และเทคโนโลยีควบคุม สาขานิติวิทยาศาสตร์ ,สภาวิชาชีพวิทยาศาสตร์และเทคโนโลยี ,6 ธ.ค 2565

#WINDOWSFORENSIC #COMPUTERFORENSICS #DFIR #FORENSICS #DIGITALFORENSICS #COMPUTERFORENSIC #INVESTIGATION #CYBERCRIME #FRAUD #วิชาชีพนิติวิทยาศาสตร์


หมายเหตุ:เนื้อหาในเว็บไซต์นี้มีขึ้นเพื่อวัตถุประสงค์ในการให้ข้อมูลและเพื่อการศึกษาเท่านั้น
* หากมีข้อมูลข้อผิดพลาดประการใด ขออภัยมา ณ ที่นี้ด้วย  รบกวนแจ้ง Admin เพื่อแก้ไขต่อไป
ขอบคุณครับ


Friday, March 1, 2024

Digital Forensics:METADATA LAB

Digital Forensics: METADATA LAB

Digital Forensics:METADATA LAB

Metadata Samples

1.Who is the artist who created this picture?


Photo with metadata
Photo by : iptc.org 
Hint:metadata2go.

2.What brand of camera did you use to take this photo?

sanyo-vpcg250.jpg

Photo by : github.com/ianare

Hint: exif.tools


GPS Samples

3.What country is this place in?

DSCN0025.jpg
Photo by : github.com/ianare
Hint: pic2map

DSCN0042.jpg
Photo by : github.com/ianare

4.What software was used to edit this photo?


preview image
Photo by :pixelpeeper.
Hint:metadata2go.

DSCN0040.jpg
Photo by : github.com/ianare

5.What is the name of the place in this picture?


Photo by : tarranprior.com
Hint: tool.geoimgr.com & Google Map


Credit: exif-samples

อ่านเพิ่มเติม:How to View and Remove Metadata from Images

* หากมีข้อมูลข้อผิดพลาดประการใด ขออภัยมา ณ ที่นี้ด้วย  รบกวนแจ้ง Admin เพื่อแก้ไขต่อไป
ขอบคุณครับ

#WindowsForensic #computerforensic #ComputerForensics #dfir #forensics
#digitalforensics #investigation #cybercrime #fraud

Thursday, February 22, 2024

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media
พร้อมเรียนรู้กลยุทธ์สำคัญที่จะช่วยให้แกะรอยอาชญากรรมเหล่านี้ได้ ผ่านการสืบค้นหลักฐานทางดิจิทัล (Digital Forensic) จากกรณีตัวอย่าง!!

Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

Computer Forensics

     คือการเก็บหลักฐาน,การค้นหา,วิเคราะห์และการนำเสนอหลักฐานทางดิจิทัลที่อยู่ในอุปกรณ์คอมพิวเตอร์และอิเล็กทรอนิกส์เช่นไฟล์ที่อยู่ในคอมพิวเตอร์,อุปกรณ์อิเล็กทรอนิกส์,โทรศัพท์มือถือรวมถึงหลักฐานดิจิทัลที่ถูกสร้างจากระบบคอมพิวเตอร์เป็นต้น ด้วยกระบวนการที่น่าเชื่อถือเพื่อให้สามารถนำข้อเท็จจริงจากการวิเคราะห์หลักฐานนาไปใช้เป็นหลักฐานที่ศาลยอมรับฟังได้ โดยหน่วยงาน หรือองค์กรที่เกี่ยวข้อง และมีอำนาจหน้าที่ตามกฎหมาย ซึ่งข้อมูลเหล่านี้สามารถนาไปใช้ระบุผู้กระทำผิดจนถึงเป็นหลักฐานในการดำเนินคดีได้

Digital Forensic พร้อมการรับมือกับ Advanced Threat

  • Problems & Challenge
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • กระบวนการจัดการพยานหลักฐาน

  • ระบุ
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

1. ระบุ 

1 ฐานความผิด - องค์ประกอบความผิด
2 ข้อสันนิษฐาน
3 อุปกรณ์คอมพิวเตอร์ที่เกี่ยวข้อง
4 ข้อมูลคอมพิวเตอร์ที่เกี่ยวข้อง
5 ประเภทความสัมพันธ์
     - ทางตรง
     - ทางอ้อม เช่น แรงจูงใจ, ความสัมพันธ์, ประโยชน์

  • การพิสูจน์ตัวตน
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media


1. สิ่งที่คุณมี Something you have
2. สิ่งที่คุณรู้ Something you know
3. สิ่งที่คุณเป็น Something you are
  • กระบวนการจัดการพยานหลักฐาน
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media
2. รักษา
1. อำนาจหน้าที่บุคคลที่จะเข้าถึง
2. ห่วงโซ่พยานหลักฐาน
3. ป้องกันการเปลี่ยนแปลง
     - การเข้าถึงทางเครือข่าย
     - ประเภทข้อมูลคอมพิวเตอร์ (Volatile Data)
     - ชนิดสื่อบันทึกข้อมูล/อุปกรณ์
     - สถานการณ์ เช่น ข้อมูลกำลังถูกลบ
  • จัดเก็บ
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media
3. จัดเก็บ
1.ทักษะ / ความรู้
2. เครื่องมือ / อุปกรณ์
3. วิธีกการปฏิบัติ
     - ประเภทอุปกรณ์ / ระบบปฏิบัติการ
     - อื่น ๆ เช่น การเก็บภาพที่กำลัง Live สด, FB post
4. การบรรจุหีบห่อ
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • พยานหลักฐานที่บุคคลภายนอก
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media


รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • วิเคราะห์
4. วิเคราะห์
1. ตั้งประเด็นการตรวจพิสูจน์ตามรูปคดี
2. กระบวนการตรวจ
     - เครื่องมือ
     - วิธีการ / หลักวิชาการ
3. ออกรายงาน
     - ข้อเท็จจริง
     - ความเห็น
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media
  • หลักการรักษาความน่าเชื่อถือ
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media
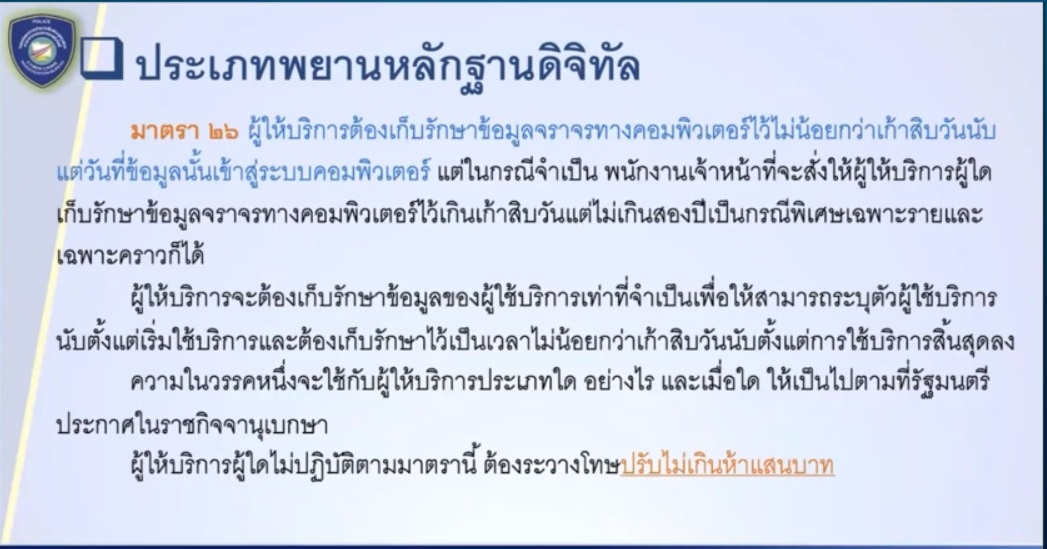
“ข้อมูลคอมพิวเตอร์” หมายความว่า ข้อมูล ข้อความ คำสั่ง ชุดคำสั่ง หรือสิ่งอื่นใดบรรดาที่อยู่ในระบบคอมพิวเตอร์ในสภาพที่ระบบคอมพิวเตอร์อาจประมวลผลได้ และให้หมายความรวมถึงข้อมูลอิเล็กทรอนิกส์ตามกฎหมายว่าด้วยธุรกรรมทางอิเล็กทรอนิกส์ด้วย (พ.ร.บ.ว่าด้วยการกระทำความผิดเกี่ยวกับคอมพิวเตอร์ฯ ม.3)
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • ประเภทพยานหลักฐานดิจิทัล
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • แบ่งตามสื่อบันทึกข้อมูล
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • แบ่งตามการะบวนการสื่่อสาร
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • แบ่งตามการเข้ารหัส
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • แบ่งตามชนิดอุปกรณ์
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • กระบวนการเกิดพยานหลักฐาน
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • การปฎิบัติงาน
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • ขั้นตอนการปฎิบัติงานที่เกี่ยวข้องกับการตรวจพิสูจน์
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

ขั้นตอนการปฏิบัติงานที่เกี่ยวข้องกับการตรวจพิสูจน์

1. รับอุปกรณ์/วัตถุพยานหลักฐานที่ต้องการตรวจพิสูจน์ พร้อมหนังสือนำส่งจากหน่วยงาน/ถ่ายภาพก่อนแกะวัตถุพยานหลักฐาน
2. ถ่ายภาพทั้งด้านหน้าและด้านหลังอุปกรณ์/วัตถุพยานหลักฐาน
3. บันทึกลงในระบบตรวจพิสูจน์หลักฐาน
4. ส่งเจ้าหน้าที่ห้องตรวจพิสูจน์หลักฐาน (Forensic) เพื่อตรวจและจัดเก็บรอดำเนินการ
5. พิจารณาว่าอุปกรณ์/วัตถุพยานหลักฐาน เป็นแบบใด และเลือกอุปกรณ์ให้ถูกต้อง
6. เมื่อตรวจพิสูจน์เรียบร้อย จัดทำรายงานผล
7. ประหน่วยงานเจ้าของเรื่องรับผลตรวจและรับของกลางคืน
8. คืนของกลางและผลตรวจให้กับหน่วยงานเจ้าของเรื่องตรวจสอบอุปกรณ์/วัตถุพยานหลักฐานให้ตรงกับที่นำส่ง เซ็นรับผลตรวจและของกลางพร้อมสำเนาบัตรเจ้าหน้าที่ที่มารับคืน

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

มาตรฐานของเครื่องมือที่ใช้ในการตรวจพิสูจน์พยานหลักฐานอิเล็กทรอนิกส์

1. กำหนดได้ (Definable)
กระบวนการตรวจพิสูจน์พยานหลักฐานใดๆ จะต้องกำหนดผลลัพธ์จากวัตถุประสงค์ที่ต้องการได้ เพื่ออธิบายกระบวนการ และรับรองความถูกต้องของกระบวนการ

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media


2.คาดการณ์ได้ (Predictable) เครื่องมือจะต้องสามารถคาดการณ์ได้ หากเครื่องมือไม่สามารถให้ผลลัพธ์ที่คาดการณ์ได้ก็เท่ากับว่าขาดความสมบูรณ์ ตามหลักการตรวจพิสูจน์พยานหลักฐานและไม่สามารถนำมาใช้งานได้

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media


3. ทำซ้ำได้ (Repeatable)
การทำงานจะต้องทำซ้ำได้ภายในขอบเขดความผิดพลาดที่เป็นที่ยอมรับ

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

4. ตรวจสอบได้ (Verifiable)
หนึ่งในหลักเกณฑ์ที่สาคัญที่สุดสาหรับเครื่องมือ ในการตรวจพิสูจน์พยานหลักฐานคือความสามารถในการตรวจสอบผลลัพธ์ที่ได้จากเครื่องมือ ไม่เพียงแต่ภายในสภาพแวดล้อมเฉพาะของการทดสอบเท่านั้น แต่ยังรวมถึงเครื่องมืออื่นๆ ในประเภทเดียวกัน ตัวอย่างเช่น ถ้าผู้ตรวจสอบคนหนึ่งในคดีใช้ซอฟต์แวร์การตรวจพิสูจน์พยานหลักฐานแบบ EnCase และผู้ตรวจสอบอีกคนหนึ่งใช้ชุดเครื่องมือซอฟต์แวร์การตรวจพิสูจน์พยานหลักฐานแบบ Forensic Tool Kit พวกเขาทั้งสองจะพบผลลัพธ์เดียวกัน

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media


รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • การวิเคราะห์พยานหลักฐาน
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • รายละเอียดของพยานหลักฐาน
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • การตั้งประเด็นคำถามการจตรวจพิสูจน์
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • ประเภทของประเด็นคำถาม
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

  • การตอบประเด็นคำถามของผู้ตรวจพิสูจน์
รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media


รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media


รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media


อ่านเพิ่มเติม:


Reference Thailand National Cyber Academy (THNCA) by NCSA

รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media

ข้อมูลจาก การอบรม NCSA Cybersecurity Knowledge Sharing ครั้งที่ 4/2567 หัวข้อ รอบรู้เรื่อง Digital Forensic พร้อมการรับมือกับ Advanced Threat และ Social Media โดย สำนักวิชาการความมั่นคงปลอดภัยไซเบอร์แห่งชาติ สกมช. ร่วมกับวิทยากรผู้เชี่ยวชาญจาก กองบัญชาการตำรวจสืบสวนสอบสวนอาชญากรรมทางเทคโนโลยี

ขอขอบคุณวิทยากร ท่าน พ.ต.ต วีระพงษ์ แนวคำดี  สว. กลุ่มงานป้องกันอาชญากรรมทางเทคโนโลยี ท่ี่ได้นำความรู้และประสบการณ์มาให้ความรู้ในงานนี้ด้วยครับ และขอนำข้อมูลมาเผยแพร่เพื่อประโยชน์ต่อไป


หมายเหตุ:เนื้อหาในเว็บไซต์นี้มีขึ้นเพื่อวัตถุประสงค์ในการให้ข้อมูลและเพื่อการศึกษาเท่านั้น ช่วยเตือนความจำ

* หากมีข้อมูลข้อผิดพลาดประการใด ขออภัยมา ณ ที่นี้ด้วย  รบกวนแจ้ง Admin เพื่อแก้ไขต่อไป
ขอบคุณครับ


#WINDOWSFORENSIC #COMPUTERFORENSICS #DFIR #FORENSICS #DIGITALFORENSICS #COMPUTERFORENSIC #INVESTIGATION #CYBERCRIME #FRAUD 

Volatility Lab

Volatility Lab  Image Wanna.vmem P.73 windows.info #python3  vol.py   -f '/home/kali/Desktop/Wanna/Wanna-MEM.vmem' windows.info     ...